
Key takeaways
- The phrase 'legally radioactive' comes from attorney Greg Ewing in MIT Technology Review. His point was that emails and calendars hold sensitive personal details, such as medical appointments and school pickup plans.
- Owning data is not the same as having the right to sell it. Customer contracts, NDAs, privacy promises and vendor license terms can all limit resale.
- The FTC has said privacy promises are enforceable and that quietly changing terms to use data for AI training can be unfair or deceptive.
- De-identification lowers risk but does not remove it. Under GDPR, data is anonymous only if no one can identify people using means reasonably likely to be used, and the 2019 research on re-identification shows how few attributes can single people out.
- Employee data is the weak point in the Spirit sale. The privacy ombudsman's review did not assess employee risks, and unions and Congress members objected on that ground.
- Security does not end at the sale. Mercor, a buyer of company data, confirmed a 2026 supply-chain attack that led to lawsuits. Ask where your data will sit and who can touch it.
Where "legally radioactive" comes from#
In its October 13, 2026 report on AI labs buying data from failed startups, MIT Technology Review quoted Greg Ewing, an attorney who advises AI startups, calling this kind of data "legally radioactive." He pointed to the sensitive details inside emails and calendars, such as medical appointments and school pickup plans.1
The warning is easy to understand with an example. A company's Slack history is not a table of products. It is thousands of people talking, some about work and some about their lives. Sell it, and you are handing the buyer a record of those people.
This page is a checklist for anyone thinking about it. It draws on the Spirit Airlines sale, where the objections came in public, and on the law as stated in primary sources. It is not legal advice, and the rules differ by place and industry. We are a broker and we have an interest in this market, so we have tried to cite everything and mark what we could not verify.
What the Spirit fight showed#
Google won an August 2026 auction for Spirit Airlines' de-identified internal data with a $10 million bid. As of October 22, 2026 the sale is not approved, and the hearing has been moved to November 6, according to IBTimes UK.2 The full account is on our Spirit Airlines page. The objections map onto the risks below.
- Unions. The Association of Flight Attendants-CWA argued that even de-identified data could expose flight attendants through patterns or small-group identifiers, and that anonymization does not guarantee privacy.3
- Lawmakers. On October 8, a letter signed by 121 members of Congress by IBTimes UK's count asked Google and Spirit to exclude employee records, timecards, payroll and Microsoft 365 content about flight attendants, protect any remaining medical, disciplinary or pay records, and order an independent review of staff confidentiality before any transfer. They cited the National Institute of Standards and Technology's view that data stripped of names can sometimes still reveal identities.2
- The ombudsman. The court-appointed consumer privacy ombudsman recommended approval on October 5 for the de-identified data, but her review did not assess risks to employees or third parties.4
- The process. The Next Web, reading the sale agreement, said the buyer can designate and pay the de-identification agent and asked who audits it. It also noted the agreement requires the data to keep "referential integrity," which the author argues makes re-identification more feasible.5
Google says it is not looking to buy any personal information from Spirit.4 The case is not decided. We use it because it surfaced the arguments in public.
The checklist#
1. Do you have the right to sell it?#
Owning data is not the same as being allowed to sell it. One analysis of micro1's program, by Pebblous, lists confidentiality clauses in customer agreements and NDAs, GDPR purpose limitation, the expired CCPA business-to-business exemption, and no-redistribution terms in vendor licenses as limits on resale.6 micro1's own page says companies must have the "internal approval processes and permissions" to participate, and Pebblous reads that as putting the burden of checking on the seller.67
Check:
- Customer contracts and NDAs: do they forbid sharing content or derivatives with third parties?
- Vendor and tool licenses: Slack, Salesforce, Zendesk and others may limit how exported data can be used.
- Third-party content in your data: customers' emails, partners' documents, licensed material.
- Acquisition or investment terms. AI Weekly's example is a startup being acquired by HubSpot that was approached by Mercor about its code and task records eight days later, with the open question of whether the acquirer's deal terms would allow it.8
2. What did you promise customers and staff?#
The Federal Trade Commission's Office of Technology wrote in January 2024 that companies that break privacy commitments to users or customers may face liability under laws the FTC enforces, that commitments in terms of service, privacy policies and promotional materials all count, and that "there is no AI exemption from the laws on the books." It also said the FTC has in past cases required companies that unlawfully obtained data to delete products, including models and algorithms, built from it.9
In February 2024 the FTC added that it may be unfair or deceptive to adopt more permissive data practices, such as sharing consumer data with third parties or using it for AI training, and tell people only through a secret, retroactive change to terms or a privacy policy.10
In the 23andMe bankruptcy, FTC Chairman Andrew Ferguson wrote in March 2025 about those concerns, saying "Consumers should be able to trust that companies will keep their promises."11
Check: read every privacy notice, employee handbook and customer promise that touched this data. If the notice says you do not share data with third parties, a sale may contradict it. Do not "fix" the notice after the fact.
3. Does it contain employee data?#
Workplace messages are about employees. The Spirit objections show that this is where scrutiny falls first. MIT Technology Review also reports that sale proceeds typically go to senior creditors and investors, not employees, and that there is no federal law banning such sales.1
California's attorney general says the CCPA exemptions for employment-related information and business-to-business data expired on December 31, 2022.12 Rules outside the US differ, and we cover the main ones in our research on legal frameworks for selling business data.
Check: whether HR files, payroll, performance notes, medical or accommodation requests, and private messages are in scope. Consider excluding them outright, as SimpleClosure says it does for sensitive employee and health records.13
4. Which privacy law applies?#
You do not need to be a lawyer to know which questions to ask. Here are three common regimes, in brief.
HIPAA (US health information). It applies to covered entities and their business associates. They may not sell protected health information except under defined authorizations. Data de-identified under the rule is not treated as protected health information.14 A regulated entity can de-identify in two ways under 45 CFR 164.514(b): expert determination, where a qualified person concludes the risk of identifying an individual is "very small" and documents it, or safe harbor, where 18 categories of identifiers are removed and there is no actual knowledge that what remains could identify someone.15
GDPR (EU and UK-style rules). Recital 26 says that to decide whether a person is identifiable you consider "all the means reasonably likely to be used," including cost, time and available technology. Pseudonymised data is still personal data if it can be linked back, and the principles do not apply to truly anonymous data.16 The UK ICO's guidance adds that identifiability is a spectrum, and it uses a "motivated intruder" test: assume a reasonably competent person with ordinary resources, such as the internet and public records, and see whether they could identify someone. It tells organizations to reassess over time as new datasets and attacks appear.17
CCPA (California). It gives consumers the right to know, delete and opt out of the sale or sharing of their personal information. It applies to for-profit businesses doing business in California that meet any of three thresholds: more than $25 million in revenue, buying, selling or sharing the data of 100,000 or more California consumers or households, or earning half their revenue from selling personal information.12 Because the employee and business-to-business exemptions have ended, those categories are in play.
Other states have their own laws. The IAPP counted 19 states with comprehensive privacy laws as of July 2025.18 We did not verify each state's treatment of employee or de-identified data, so ask.
5. Will de-identification hold?#
De-identification lowers risk and does not remove it. The National Institute of Standards and Technology wrote in 2015 that researchers have shown some de-identified data can still be re-identified.19 A 2019 Nature Communications paper estimated, with a statistical model, that 99.98% of Americans could be correctly re-identified in a dataset with 15 demographic attributes. That is a model-based estimate, and the paper's body ties the figure to uniqueness in Massachusetts, so it is best read as a warning, not a measured rate for any dataset.20
Free text is harder than a table. A name is easy to remove, but a story about a particular person's day is not. The Spirit union objection about small groups, such as a crew base, is the same issue.3
Check:
- What method is used (rules, models, human review), and what is its measured miss rate on a sample you can inspect?
- Who certifies it, and who pays them? In Spirit's case, the ombudsman wanted a certification filed before every transfer and asked that it state how many passengers' details were found and removed.4
- Does the contract bar the buyer from re-identifying and from passing the data on without the same commitment? The ombudsman asked for exactly that.4
- Does the process keep records linked across systems? That helps a model learn how work flows, and it also makes re-identification easier, as The Next Web argued.5
- Will anyone re-test as new datasets and attacks appear, as the ICO advises?17
micro1 says it removes personal information "when relevant" and uses synthetic rewrites for some datasets, and lets companies review representative samples before use.7 Mercor says its platform extracts and de-identifies data in an automated process and that no AI lab buyer or third-party vendor sees raw data.21 Those are statements by the buyers. Ask for the evidence.
6. Who holds the data afterward, and how safe is it?#
A sale moves risk to a new custodian. In March 2026, Mercor confirmed a security incident tied to a supply-chain attack on the open-source LiteLLM library. The extortion group Lapsus$ claimed to have Mercor data and shared a sample that TechCrunch reviewed, which allegedly included material referencing Slack data and apparent ticketing data. Mercor declined to say whether customer or contractor data was accessed.22
Mercor later said in a June 25, 2026 update that of nearly five million experts only a very limited subset had sensitive information affected, that impact on customer information was very limited, and that no employee data was affected. It also said it had completed an investigation and offered identity protection to notified experts.23 Several contractor class actions were filed from April 1, according to HR Dive.24
We are not saying Mercor mishandled any company's data. The point is that a buyer's security record matters, and that this is a live example of a data buyer being targeted. The Spirit ombudsman said that if the court considered Mercor's bid, she wanted to examine Mercor's 2026 incident.4
Check: where the data will be stored, who can access it, how it is isolated from other clients' data (micro1 says it uses isolated pipelines),7 what happens in a breach, and whether you get notice.
7. Is the company in or near bankruptcy?#
Different rules apply. In a US bankruptcy, a trustee generally cannot sell personal information if the debtor promised customers it would not share it with outsiders, unless the sale is consistent with that policy or a consumer privacy ombudsman is appointed and the court approves after a hearing.25 That is what happened at Spirit. We did not find a source on the rules for a non-bankruptcy dissolution, so a lawyer should answer that.
8. What does the contract say?#
The AI Weekly editor's note recommends explicit data-disposition terms in deal documents, for both founders and acquirers.8 On a data sale, the clauses to check are:
- Scope. What data, from when, with which exclusions in writing.
- Use. Field of use, no re-identification, no onward transfer without equal commitments.
- Exclusivity. Pebblous notes micro1 has not published its exclusivity wording or its liability and indemnity terms.6
- Security. Standards, audits, breach notice.
- Deletion. micro1 says data is deleted on request or at the end of the engagement; get that in the contract.7
- Indemnity. Who pays if the data turns out to have been unsellable.
- Payment. Mercor says payment is by wire after delivery, typically two to four weeks after signing.21 Terms differ by buyer.
A scorecard you can use#
Table 1. A quick risk screen. If you answer "no" or "do not know" to a row, stop and resolve it before talking price.
| Question | If no or unknown |
|---|---|
| Have we read every customer contract that touches this data? | Do not share |
| Does any privacy notice or staff policy forbid this sale? | Do not share |
| Have we excluded HR, payroll, health and private messages? | Exclude them |
| Do we know which privacy laws apply? | Ask counsel |
| Can we inspect de-identification results on a sample? | Ask for one |
| Do we know where the data will be stored and who sees it? | Ask the buyer |
| Does the contract cover re-identification, onward transfer and deletion? | Add them |
The assessment can help you sort data types before you start, and our main guide goes deeper on rights, privacy and pricing. For the market side, see our look at what is actually documented about broker earnings and the deal tracker.
Bottom line#
"Legally radioactive" is one lawyer's phrase, and it is blunt. It is also a fair summary of what the Spirit fight showed: employees, privacy law and re-identification risk all sit in the same archive. Companies that sell well will be the ones that know their rights first, strip out what they cannot clear, test the de-identification and pin the buyer down in writing.
SellYourAIData has no deals or partnerships with any company named here. This is general information and not legal advice.
Frequently asked questions
It is the phrase attorney Greg Ewing used in MIT Technology Review for workplace data from failed companies. His point was that emails and calendars carry sensitive details about people, so the data creates legal exposure for anyone who handles it.
Not always. Ownership is not the same as permission to sell. Customer contracts, confidentiality clauses, privacy notices, employee agreements and vendor licenses can restrict resale. Check each before you talk to a buyer.
Safer, not safe. HIPAA, GDPR and California law each set conditions for treating data as de-identified or anonymous, and researchers have repeatedly re-identified data thought to be anonymous. Contracts should also bar the buyer from re-identifying people.
There is no single rule we can cite. Employee data is covered by California's privacy law now that its employment exemption expired, and rules outside the US differ. Unions and lawmakers pressed hard on this in the Spirit sale. Ask a lawyer, and tell employees what you plan.
That depends on the contract, and it is a reason to negotiate it. The Mercor incident shows a data buyer can be breached. Ask for security commitments, restrictions on onward transfers, deletion rights, audit rights and indemnity.
No. It is a plain summary of public sources. Rules vary by country, state and industry, so use a lawyer for any actual sale.
Sources
Every numbered reference above points to an entry here. Figures come from these pages as of the date shown at the top of the article. Where a source reports a number it got from unnamed people, the text says so.
- AI labs are buying data from dead startups to train their models (MIT Technology Review, October 2026)
- US lawmakers urge Google to strip Spirit staff's medical and disciplinary files from AI deal (IBTimes UK, October 2026)
- Flight attendant union opposes Google's Spirit data bid (InsideFlyer, August 2026)
- Spirit's privacy ombudsman backs Google's $10m data deal (The Next Web, October 2026)
- Google picked and paid for the firm anonymising the Spirit Airlines data (The Next Web, August 2026)
- micro1 Company Data Partnerships: rights analysis (Pebblous, October 2026)
- micro1 Data Partnerships (micro1, accessed October 2026)
- Mercor chases shuttered startups' Slack and Jira archives (AI Weekly, August 2026, summarizing reporting by The Information and Forbes)
- AI Companies: Uphold Your Privacy and Confidentiality Commitments (Federal Trade Commission, January 2024)
- AI (and other) Companies: Quietly Changing Your Terms of Service Could Be Unfair or Deceptive (Federal Trade Commission, February 2024)
- FTC Chairman Andrew N. Ferguson Issues Letter on 23andMe Bankruptcy and Impact on Consumer Data (Federal Trade Commission, March 2025)
- California Consumer Privacy Act (CCPA) (California Attorney General, accessed October 2026)
- SimpleClosure AssetHub on track to return $10M+ to venture-backed startups (Business Wire release via 01net, September 3, 2026)
- 45 CFR 164.502: Uses and disclosures of protected health information, general rules (Cornell Law School Legal Information Institute, accessed October 2026)
- 45 CFR 164.514: Other requirements relating to uses and disclosures of protected health information (Cornell Law School Legal Information Institute, accessed October 2026)
- Recital 26: Not applicable to anonymous data (Intersoft Consulting, unofficial text of Regulation (EU) 2016/679, accessed October 2026)
- How do we ensure anonymisation is effective? (Information Commissioner's Office, accessed October 2026)
- US State Privacy Laws Overview (International Association of Privacy Professionals, last updated October 27, 2025)
- NIST IR 8053: De-Identification of Personal Information (National Institute of Standards and Technology, October 2015)
- Estimating the success of re-identifications in incomplete datasets using generative models (Nature Communications, July 2019)
- Your enterprise data can advance frontier AI (Mercor, accessed October 2026)
- Mercor says it was hit by cyberattack tied to compromise of open source LiteLLM project (TechCrunch, March 2026)
- Update on Mercor security incident (Mercor, June 2026)
- AI industry recruiting platform faces multiple lawsuits over data breach (HR Dive, April 2026)
- 11 U.S. Code 363: Use, sale, or lease of property (Cornell Law School Legal Information Institute, accessed October 2026)
About the author
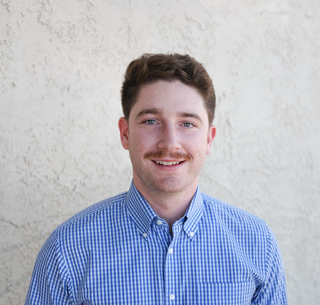
Josh Bernstein is an AI expert and the co-founder and managing partner of SellYourAIData, where he leads buyer relationships and deal strategy. He works with AI every day: he builds the AI agents, large language model content systems and data pipelines that run Something Inc., the SEO and AI search agency he co-founded, which has served more than 95 companies. His focus there is how AI models find, read and cite company information, which is the same question AI buyers ask when they license data. Before that he spent more than ten years running search and growth programs for B2B technology, SaaS, ecommerce and Fortune 500 brands.
- Co-founder and Managing Partner, SellYourAIData
- Co-founder, Something Inc. (SEO and AI search, 95+ companies served)
- Builds AI agents, LLM content systems and AI search visibility tools
- 10+ years in search and growth for B2B and Fortune 500 brands
 Appenvs
 Toloka
 Handshake AIvs
 Mercor